Free Vulnerability Scan — Pick Your Compliance Standard
OpenVAS-powered scan against up to 500 IPs. No credit card. No software to install. Pick the standard you need — your PDF lands in the portal the instant the scan finishes.
CERT-In · ISO 27001 · RBI · SEBI CSCRF · DPDPA · PCI-DSS — same scan, your choice of report format. Same data, mapped to whichever framework your auditor expects.
This is what your free report looks like
Anonymised sample from an actual scan. Severity counts, CERT-In mapping, per-CVE remediation. Not stock — real output from the same engine that scans your environment.
▶ Download the full 16-page sample report (PDF)
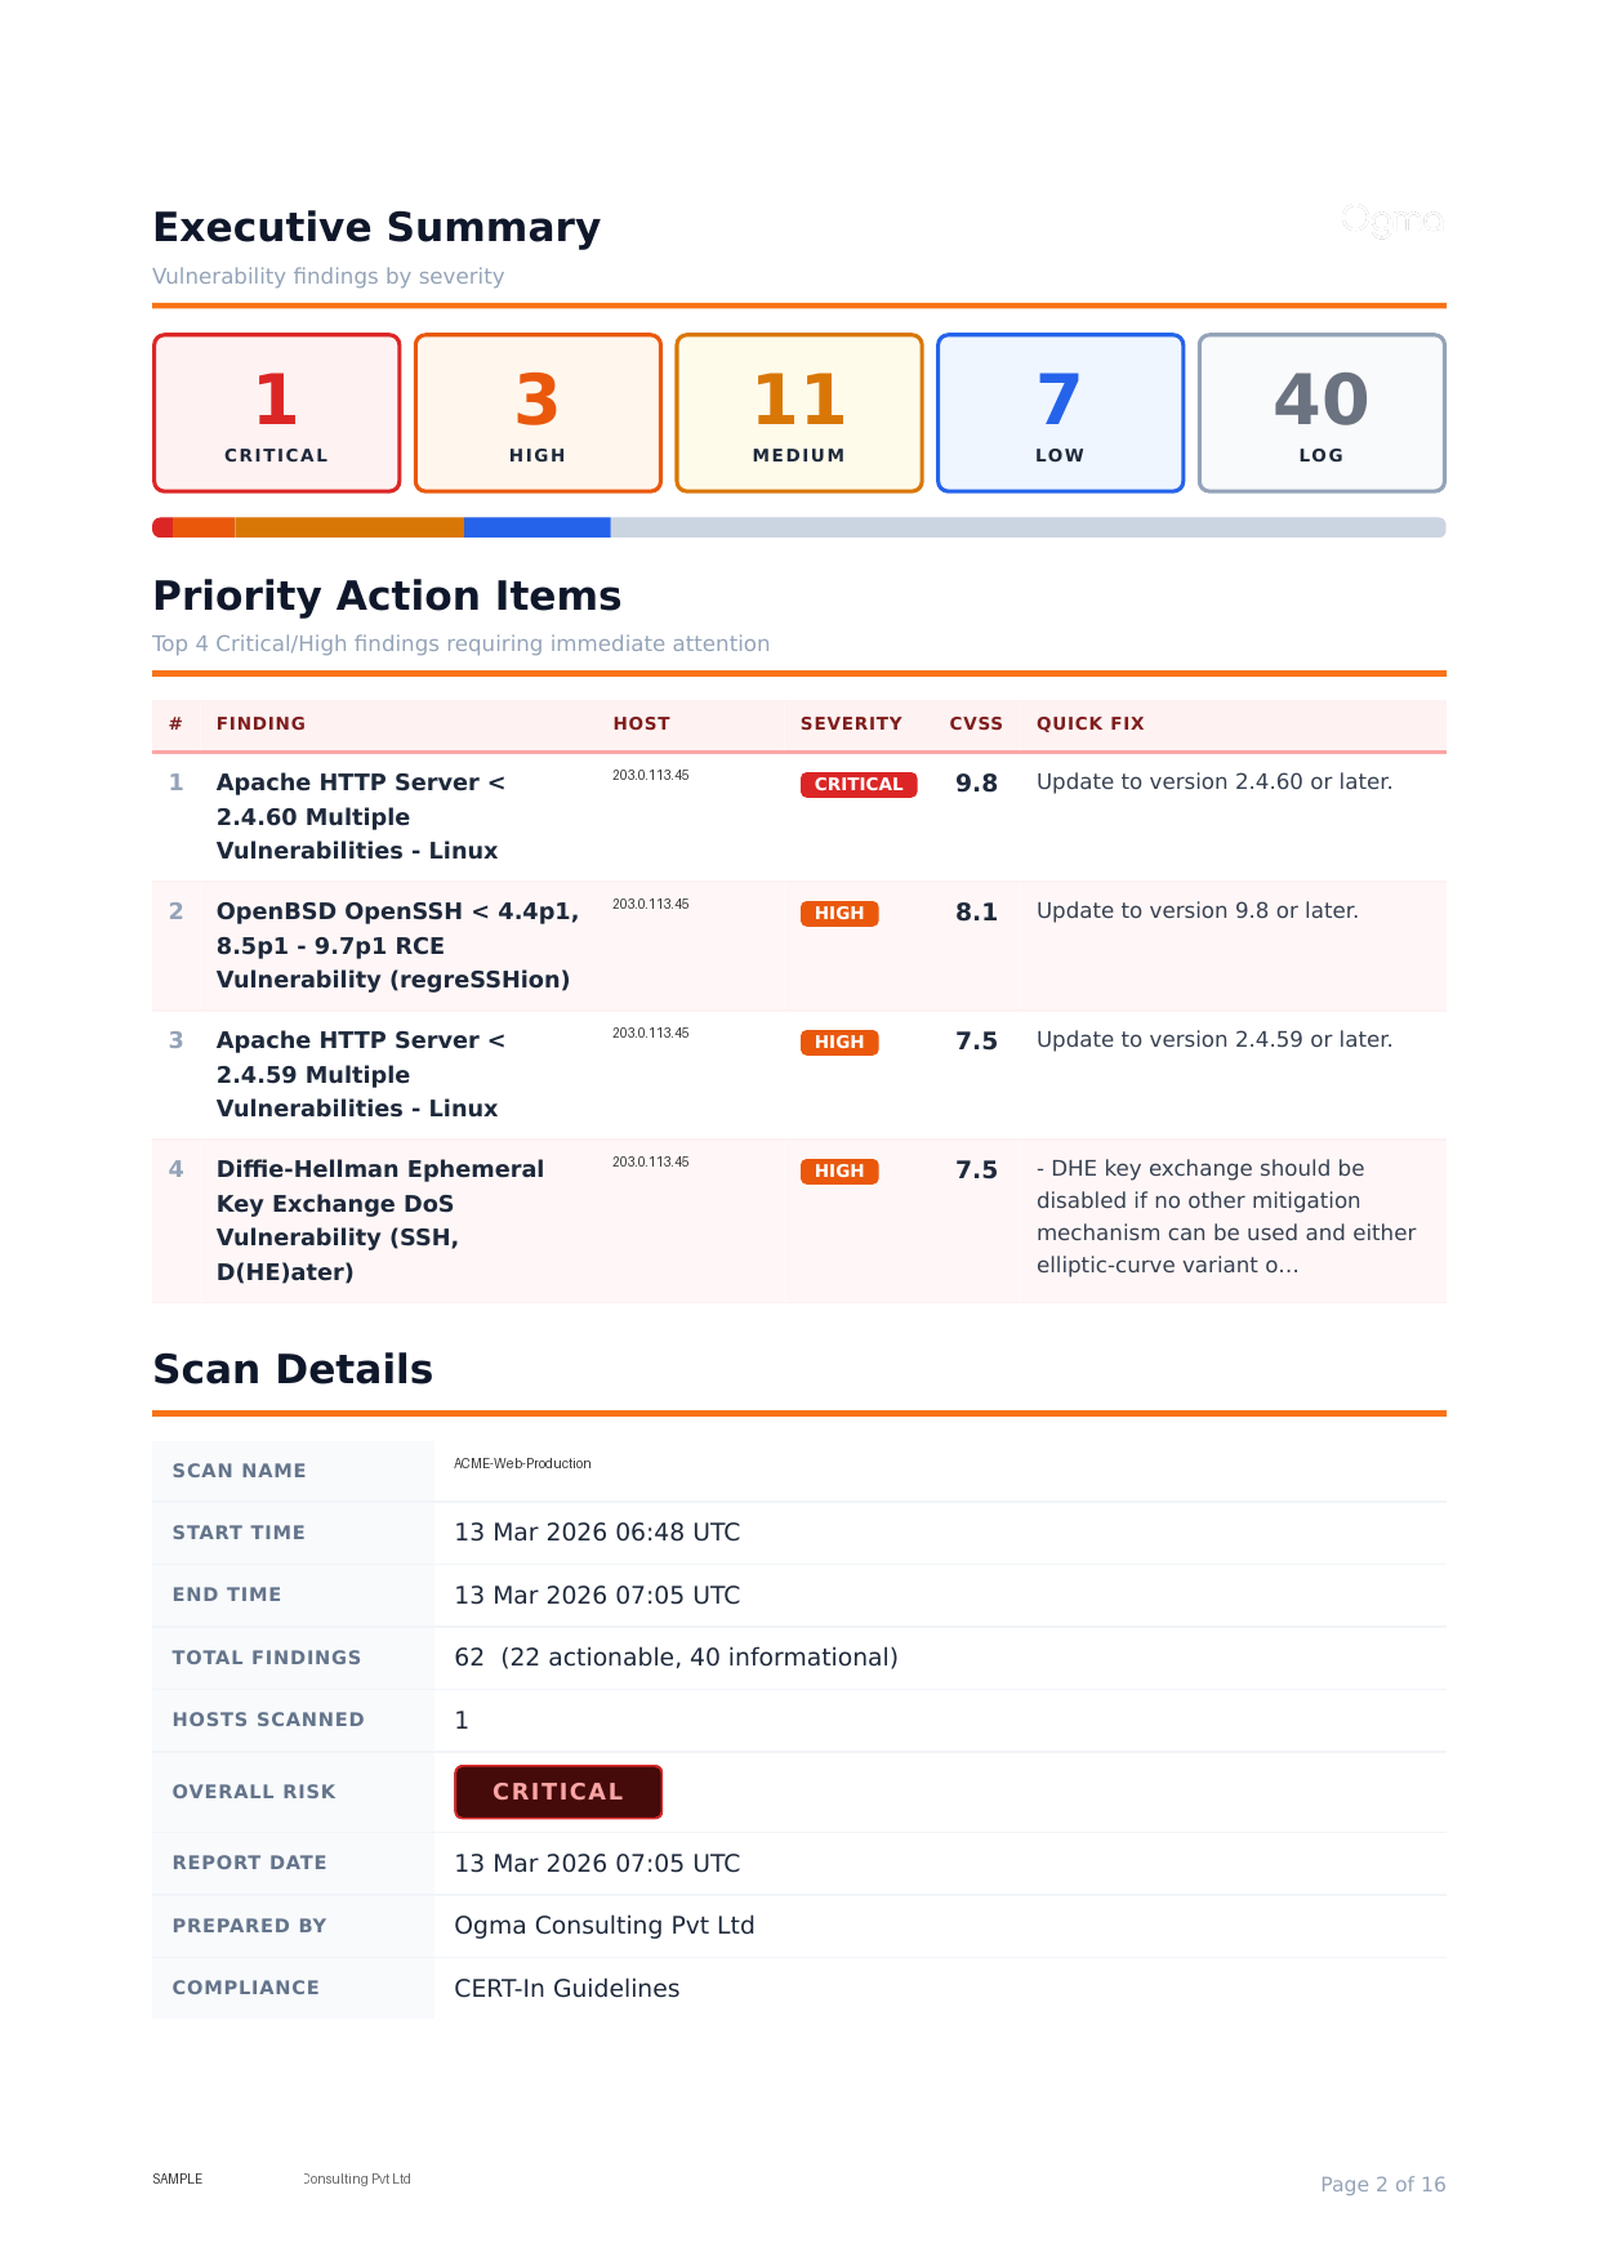
Page 2 · Executive Summary
Severity counts + Priority Action Items
Critical / High / Medium / Low / Log counters, plus the top 4 actionable findings with CVSS score and a one-line fix.
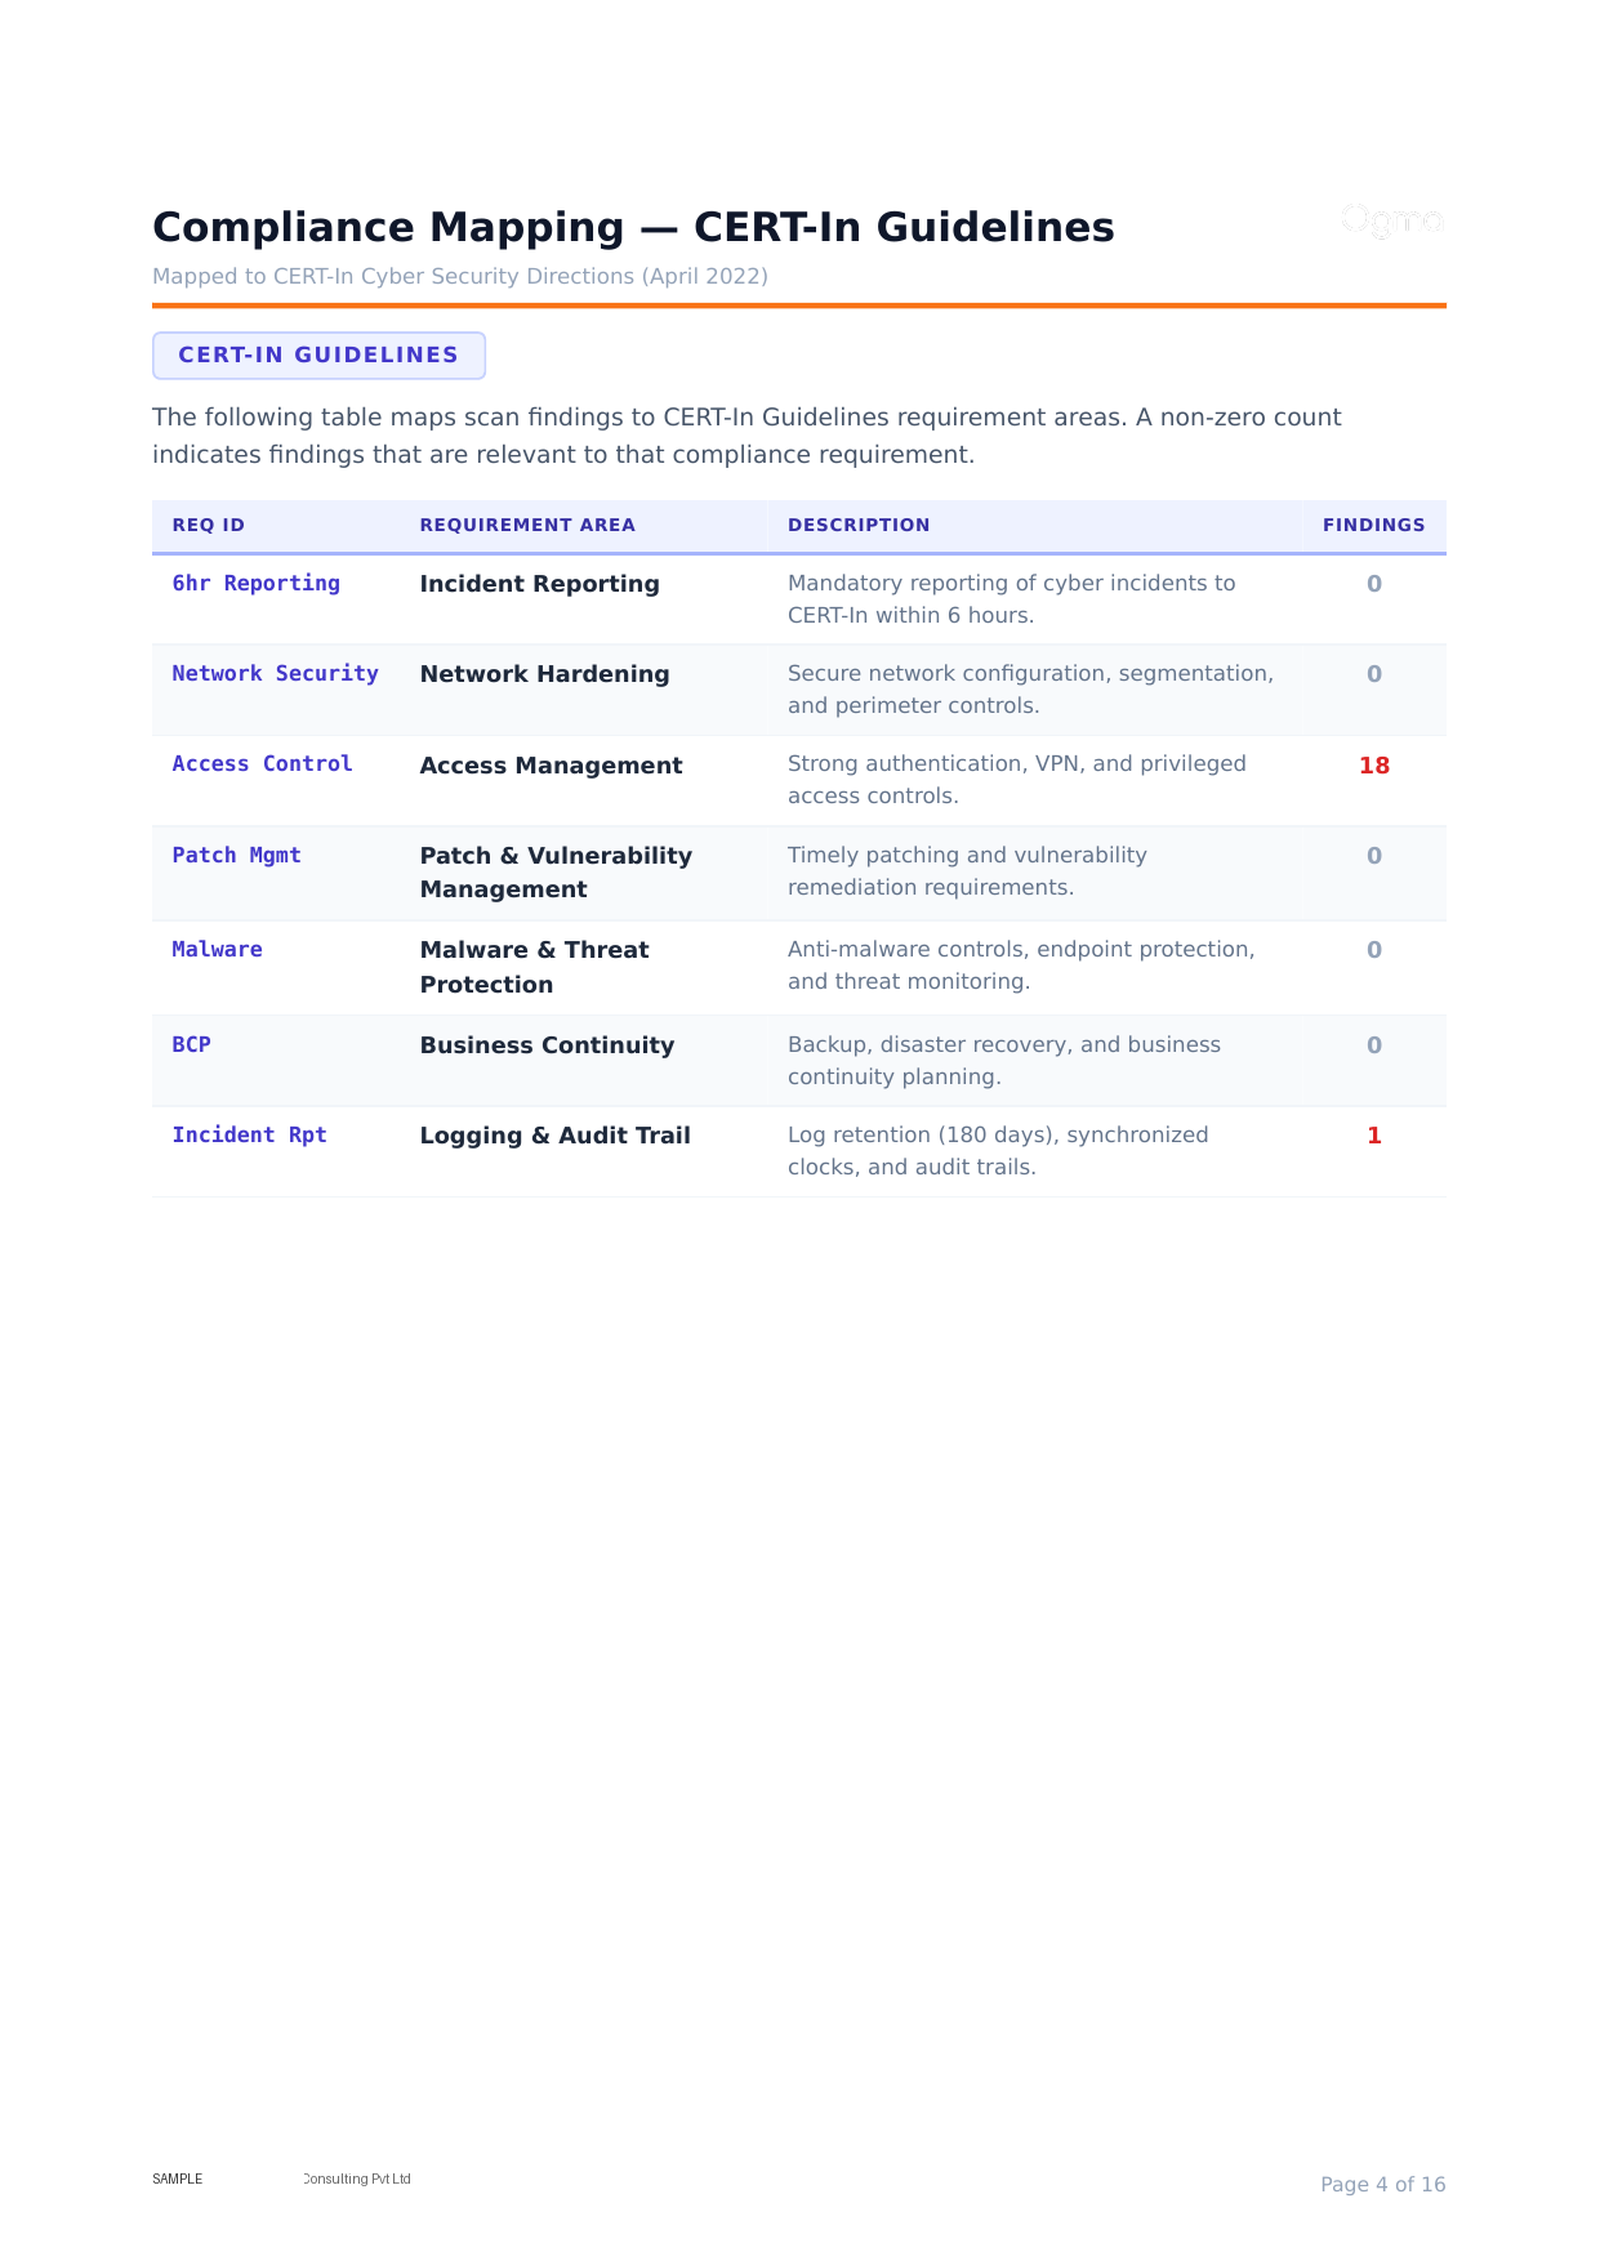
Page 4 · Compliance Mapping
CERT-In Guidelines Coverage
Findings mapped to seven CERT-In requirement areas — Incident Reporting, Network Hardening, Access Management, Patch Management, Logging & Audit Trail.
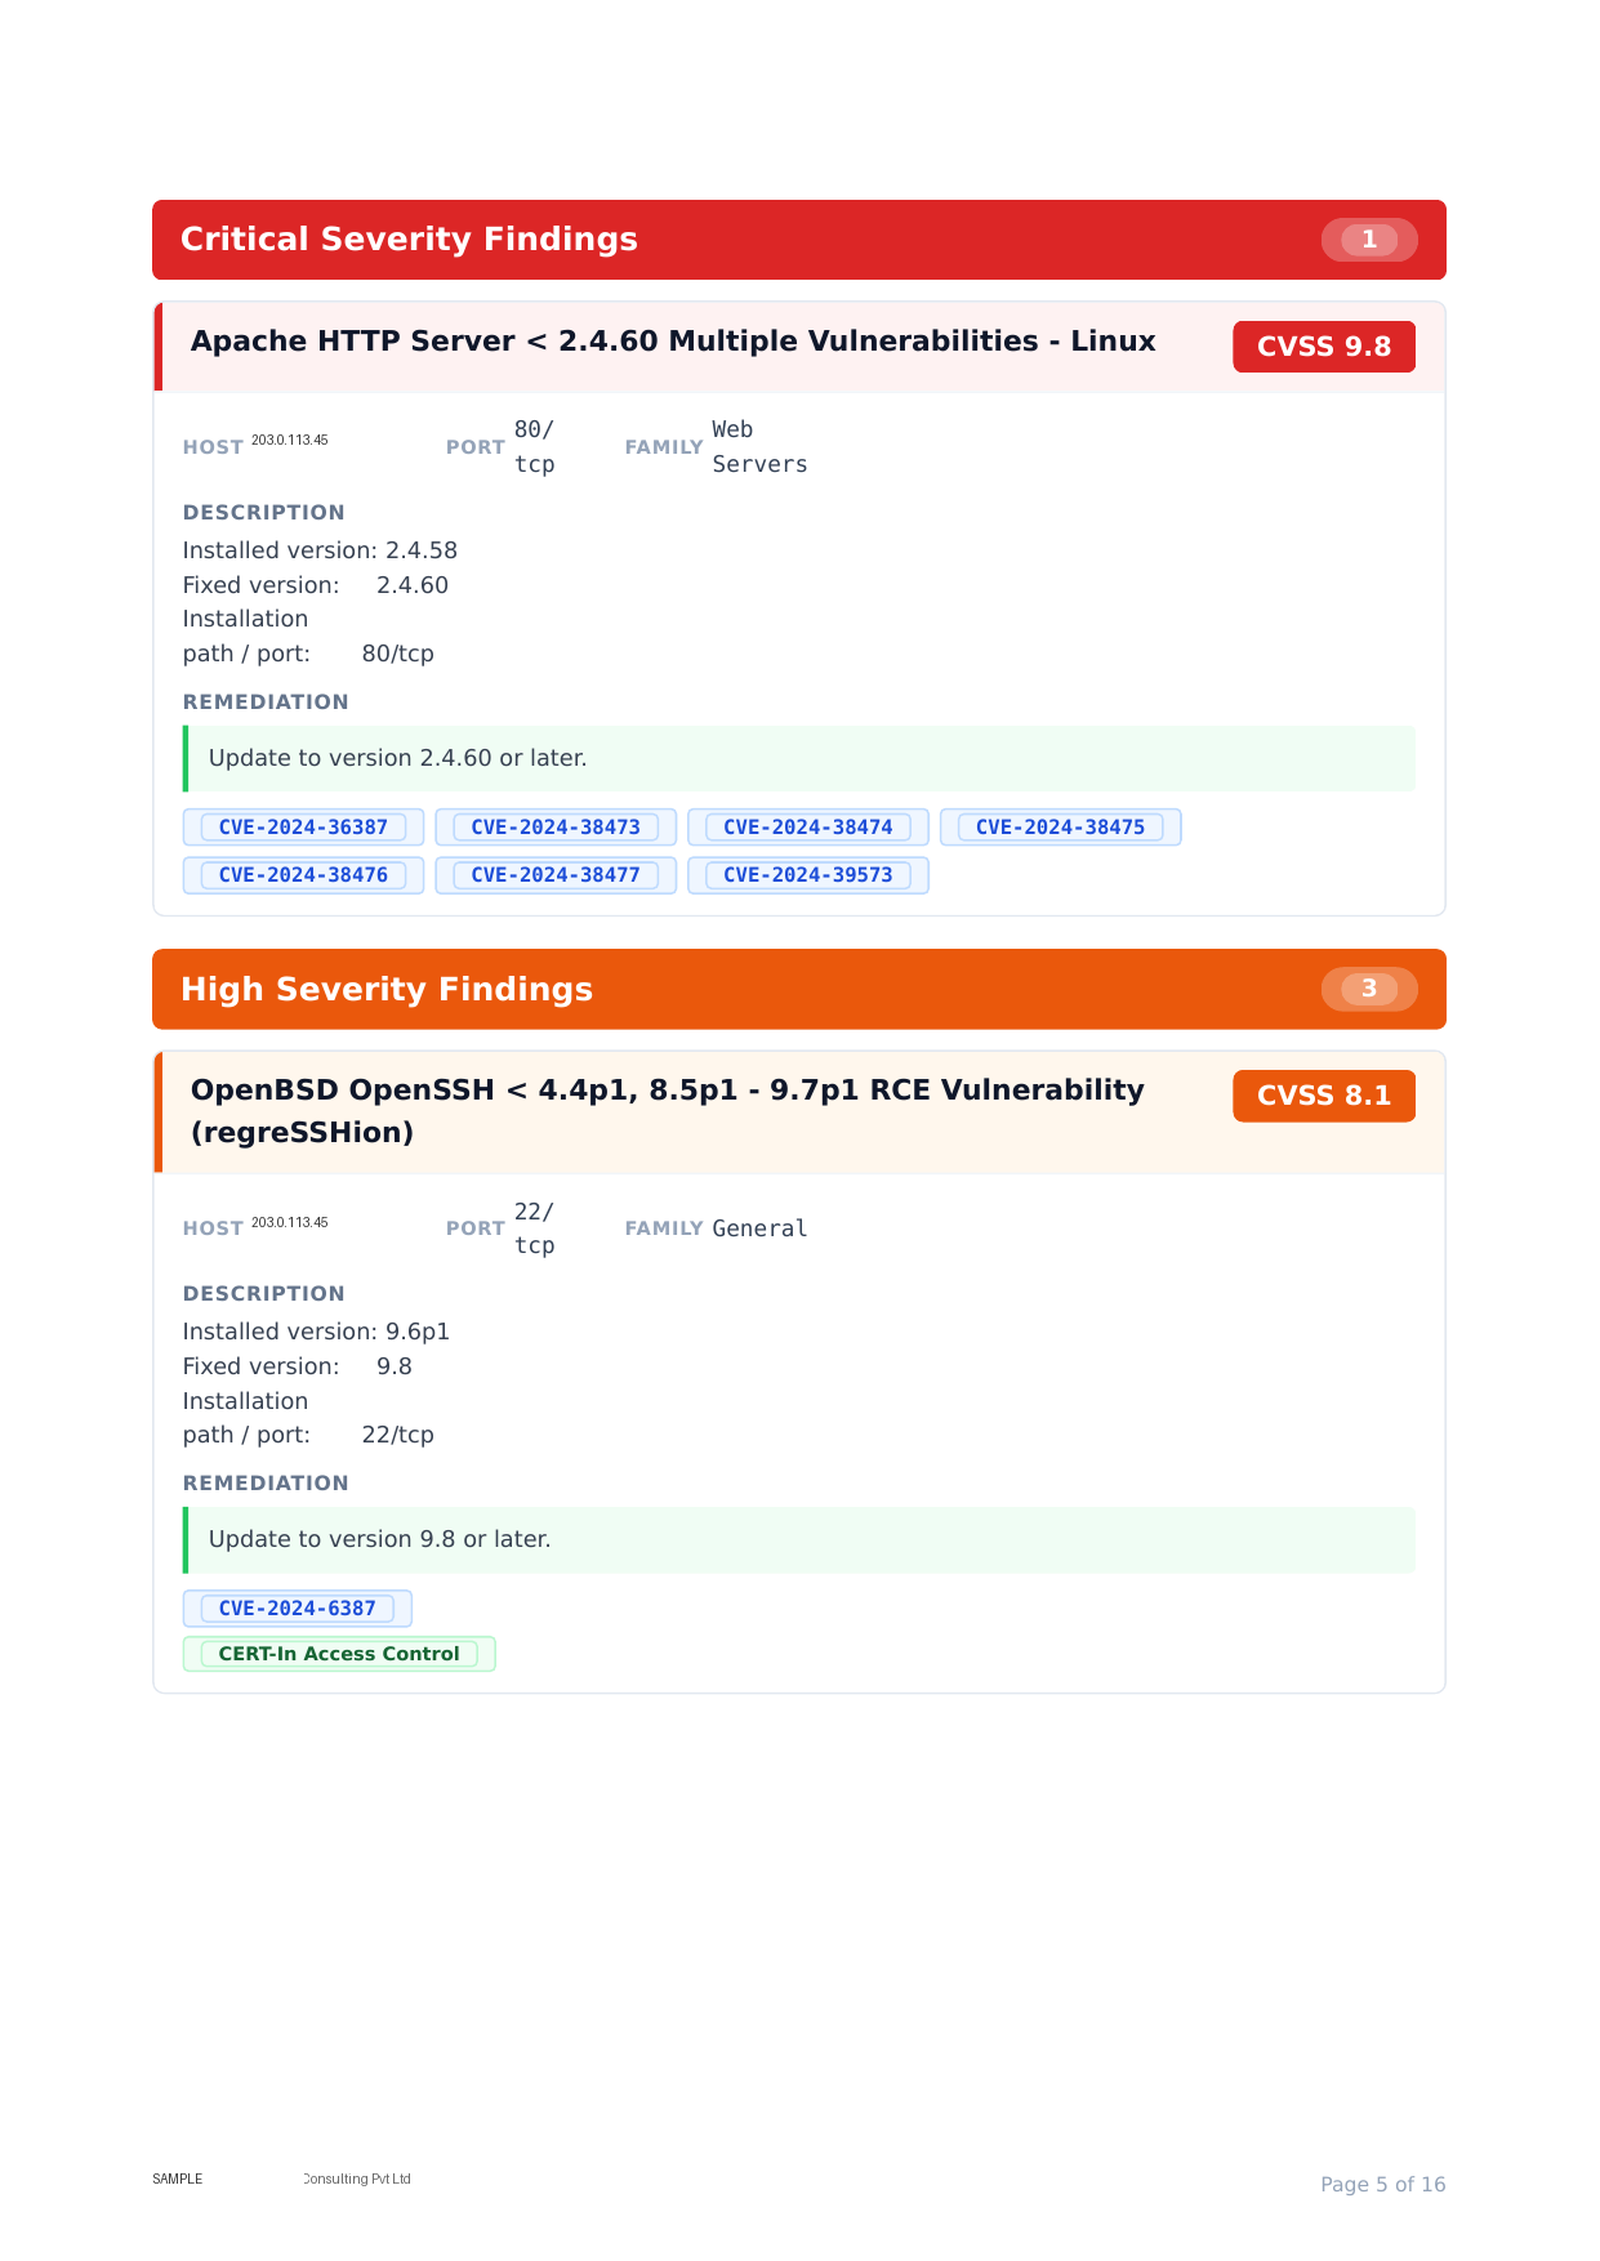
Page 5 · Finding Detail
Per-CVE remediation
Each finding with host, port, family, installed vs fixed version, plain-English remediation, and every relevant CVE chip.
What's in your free PDF
Findings report — instant on scan completion. No 24-hour wait, no phone call, no sales playbook.
Deliverable 1
Findings PDF (multi-standard)
Branded report by Ogma — Executive Summary, Priority Action Items, Compliance Mapping in your chosen framework, full per-finding cards. Generated the moment the scan completes.
Deliverable 2
CVE List with CVSS
Every finding with CVSS v3 score, host, port, fixed version, CVE chips. Sortable in your portal account.
Deliverable 3
Compliance Mapping (your standard)
Findings mapped to CERT-In · ISO 27001 · RBI · SEBI CSCRF · DPDPA · PCI-DSS — pick the framework that matches your audit, regenerate the PDF in seconds.
Deliverable 4
Portal Access (Permanent)
Browse findings, download reports in any format, re-run scans (subject to free-tier cooldown). Your account stays free.
▶ Detailed remediation reports (prioritised step-by-step fix plans, sign-off workflow, attestation letter on Ogma letterhead) are a paid add-on generated on request — not part of the free tier. Ask in the portal once your scan completes.
How it works
Four honest steps. No software install. No firewall changes from your side.
Free covers findings. Pro covers remediation + attestation.
Free gives you the findings PDF in any compliance format the moment your scan completes — perfect for "what does an attacker see." Pro adds the remediation plan, analyst triage, sign-off workflow and a partner-attestation letter your auditor will accept.
| What you get | Free Tier (this page) | VA Pro · ₹49,999/qtr |
|---|---|---|
| Scan scope | up to 500 IPs | up to 250 IPs · Tenable + OpenVAS dual |
| Scanning engine | OpenVAS | Tenable + OpenVAS (dual lookup) |
| Findings PDF | ✓ Instant on scan completion | ✓ Instant + analyst-triaged in 4 hrs |
| Compliance format choice | ✓ CERT-In · ISO 27001 · RBI · SEBI CSCRF · DPDPA · PCI-DSS | ✓ Same — plus auditor walkthrough |
| Analyst triage (false-positive removal) | — | ✓ Senior NSE7 analyst |
| Detailed remediation report (prioritised step-by-step fixes) | paid add-on, on request | ✓ Included every quarter |
| Remediation sign-off workflow | — | ✓ Audit-trail tracker |
| Auditor-ready attestation letter | — | ✓ On Ogma letterhead |
| Scan cadence | 1 free scan / 30 days | Monthly + on-demand |
| Cost | Free, forever | ₹49,999 / quarter |
Compliance relevance — at a glance
Indian regulators don't accept "we use a firewall" as evidence. They want a dated VA report in the format they recognise. Same scan, six standard mappings — pick yours when the report renders.
DPDPA
Section 8(5) — Reasonable Security Practices
Periodic vulnerability assessments are explicitly named as part of "reasonable security safeguards" expected of every Data Fiduciary.
RBI
Master Direction on IT Governance
Banks, NBFCs and PPI issuers must maintain a "comprehensive vulnerability management programme" with documented periodic assessments.
SEBI
Cybersecurity & Cyber Resilience Framework
Listed entities, mutual funds, depositories and stock brokers — annual VA + half-yearly external scan, in CERT-In format.
ISO 27001
Annex A.12.6.1 — Technical Vulnerability Management
A documented process for receiving information about technical vulnerabilities and acting on them is mandatory for certification.
Frequently asked questions
Honest answers. If something isn't covered, just email [email protected] — Pawan answers personally.
Why is this free? What's the catch?
No catch. Ogma is an Authorised Fortinet Partner that runs vulnerability assessments for Indian enterprises every day. Free-tier scans are cheap for us at scale and produce a real findings report that proves we know what we're doing. The two paid upgrades are honest: (1) detailed remediation reports (prioritised step-by-step fix plans, sign-off workflow, attestation letter) charged per request — and (2) VA Pro for ongoing scans + analyst triage + everything in #1 included. Most free-tier users stay free forever.
How fast does the magic-link email arrive?
In the same second you submit the form, we issue an invite token and queue the email. With Mailgun's typical delivery, you should see it in your inbox within 1-2 minutes. If 5 minutes go by and nothing's there, check spam — or write to [email protected] and we'll send it manually.
How long does the actual scan take? When does the PDF arrive?
Two distinct timings:
Scan setup — our VA team verifies the consent + target authorisation and queues the scan on your account. This is the only manual step today, capped at ≤ 1 business hour.
Scan duration — typically 1-6 hours depending on scope (50 IPs vs 500 IPs, basic vs deep). OpenVAS runs from our infra; no agent on your side.
Report — generated instantly the moment the scan finishes. Lands in your portal AND inbox. You can re-render the same scan in any of 6 compliance formats (CERT-In, ISO 27001, RBI, SEBI CSCRF, DPDPA, PCI-DSS) without re-scanning.
Is OpenVAS as good as Tenable / Nessus / Qualys?
For unauthenticated network-perimeter scans against common services (web servers, SSH, mail, databases), OpenVAS is genuinely competitive — same NVTs, similar CVE coverage. Where Tenable wins is authenticated scans, agent-based scanning, and false-positive triage by their threat-intel team. That's why our Pro tier runs both engines and our analysts triage manually.
Will the scan break my production system?
Default OpenVAS profile is unauthenticated and non-intrusive — discovery + version detection + CVE matching. We do not run brute-force, fuzzing or DoS plugins by default. If you have a particularly fragile system, tell us in the consent box and we'll throttle further.
What targets are off-limits?
Anything you're not authorised to scan. We require explicit written authorisation (the consent checkbox above counts) and we will not scan a target if your domain or IP looks like it belongs to someone else (e.g. a hosting provider, a CDN, or another company's owned infrastructure).
Do you store our scan results?
Yes — encrypted at rest in our portal so you can re-download or compare against future scans. We never share scan results with third parties. You can request deletion any time and we comply within 7 days. All data hosted in India.